





Offshore / Onsite
Hire Dedicated Team
Access a dedicated team of engineers and QA, on-site or remote, focused on your product and your roadmap.
Get StartedQA and security testing: automated regression on the paths that lose money, penetration testing with the fixes actually shipped, dependency and secret scanning in CI, and accessibility audited to WCAG 2.2 AA. A suite nobody trusts is worse than no suite at all.
Our Clients










Almost every team we meet has a test suite and does not rely on it. The failure is rarely too little testing — it is testing arranged so that green means nothing and red gets rerun until it passes.
A suite that fails randomly trains everyone to ignore red, which removes the only value a suite has.
Flakes treated as defects with an owner and a deadline. A test that cannot be made reliable is deleted rather than tolerated.
Ninety per cent coverage of getters and constructors, and nothing on the checkout path. The number is met and the risk is untouched.
Coverage argued per risk: what costs money or reputation when it breaks gets deep coverage, the rest gets very little.
Nobody runs it locally, so failures are found after merge and the feedback loop is measured in hours.
Fast unit and integration tests on every commit, the slow end-to-end layer kept small and parallelised.
A penetration test produced ninety issues, three were fixed, and the report is quoted in sales calls regardless.
Findings triaged with your engineers and fixed within the engagement, with a retest to confirm rather than a status update.
Testing and security are the same discipline seen from two angles: both are about knowing what breaks before a customer does.
Written down: which paths get end-to-end coverage, which get integration tests, and which deliberately get none. A strategy nobody wrote is a strategy nobody follows.
Auth, payment, permissions and data writes covered end to end, fast enough that nobody is tempted to skip the suite.
Existing flaky tests fixed or removed, with quarantine and ownership so the suite becomes trustworthy rather than tolerated.
Dependency, container, secret and infrastructure-policy scanning that fails the build, plus SAST on the code paths that matter.
Manual testing against your real threat model, then the fixes shipped and retested within the engagement.
Automated checks plus real screen reader passes, remediated at component level so every screen inherits the fix.
Quality work is almost always bought after an event. These are the events.
Something reached customers that tests should have caught, and the post-mortem action was "add more tests" with no strategy.
A security questionnaire, penetration test report or SOC 2 evidence is now a condition of closing.
Two thousand tests, frequent flakes, and a team that reruns until green. Nobody trusts the signal.
A legal letter or a regulator, and the audit finds hundreds of component-level issues.
Manual regression takes three days, so releases became monthly and each one carries more risk than the last.
A critical CVE, and nobody can quickly answer whether you are affected or where it is used.
Test writing is where budgets get cut first, because it is high volume and feels lower value than features. Generating the mechanical layer changes the arithmetic: edge cases from type signatures, page objects per screen, fuzzing inputs, scanner output triaged into a ranked list. The result is that coverage stops being the thing that gets sacrificed when a sprint tightens.
Boundary and error cases enumerated from type signatures and API contracts — the null, the empty array, the huge number, the malformed date. Tedious to write and exactly where defects live.
Static analysis and dependency output deduplicated, assessed for reachability and ranked by real exploitability. Untriaged scanner noise is why security reports get ignored.
Page objects and selectors updated across a suite after a UI change. This maintenance burden is the most common reason a suite is abandoned.
Whether a finding is genuinely reachable, and what it would cost you, is a judgement about your architecture and your business. Manual penetration testing is done by humans, because the interesting vulnerabilities are chains no scanner reports.
See our AI practiceAutomated scanning is a floor. The findings that matter are multi-step logic flaws, and those are found by a person thinking adversarially.
Scanner output is confirmed reachable in your context first. Unverified findings destroy the credibility of the whole report.
A test that always passes is worse than no test. An engineer confirms each one can actually fail on the defect it targets.
Automated tooling catches roughly a third of issues. Screen reader and keyboard passes are done by hand, every release.
The first improvement to most suites is subtraction: removing flaky and worthless tests so that red means something again. Only then is it worth adding coverage.
What the suite covers, what it does not, how often it flakes and how long it takes. Alongside a risk map of what actually costs money when it breaks.
Which layers cover what, which paths get end-to-end tests, and what deliberately goes untested. Agreed with engineering so it survives the next deadline.
Flaky tests fixed or deleted, the suite parallelised and brought under a time budget. A trustworthy fast suite beats a comprehensive ignored one.
Regression coverage on the money paths, plus dependency, secret, container and policy scanning that fails the build rather than filing a ticket.
Manual penetration testing against your threat model, then remediation with your engineers and a retest to confirm. A report with unfixed findings is not a deliverable.
Running inside your pipeline, in your accounts. Everything we set up is something your team can keep operating without us.


Running inside your pipeline, in your accounts. Everything we set up is something your team can keep operating without us.


Running inside your pipeline, in your accounts. Everything we set up is something your team can keep operating without us.


Running inside your pipeline, in your accounts. Everything we set up is something your team can keep operating without us.


Running inside your pipeline, in your accounts. Everything we set up is something your team can keep operating without us.



Case Studies
Selected work for retail, banking, telecom and defence teams, from brand identity and mobile apps to data platforms and AI assistants.
Panda
Reworked search, categories and checkout in Panda’s live app and website, in Arabic and English.
EDGE Group
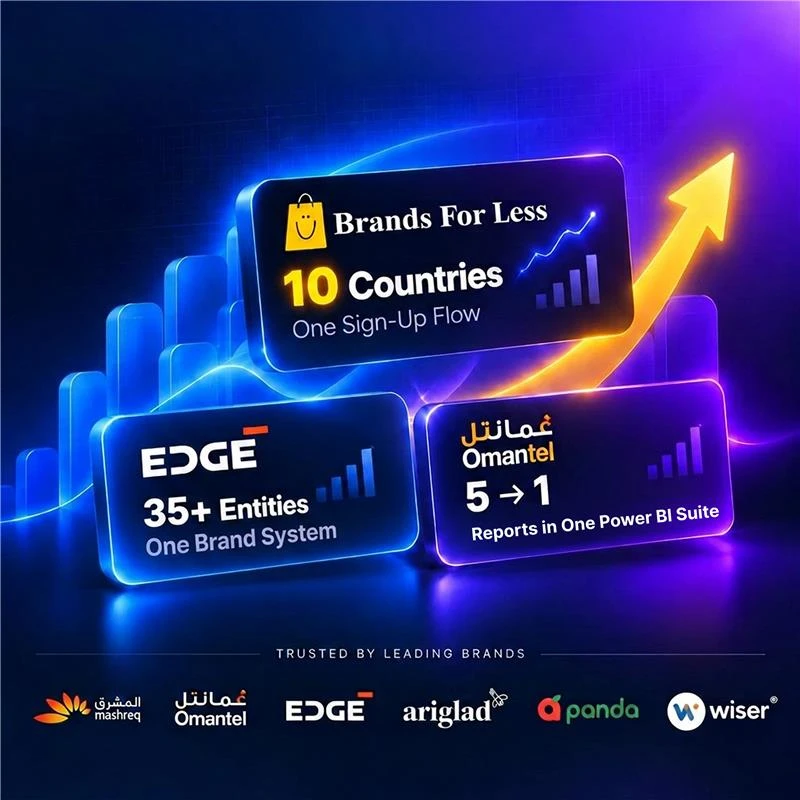
Brand identity, website and print for a group of 12,000 staff, carried onto the IDEX show floor.
Mashreq NEO
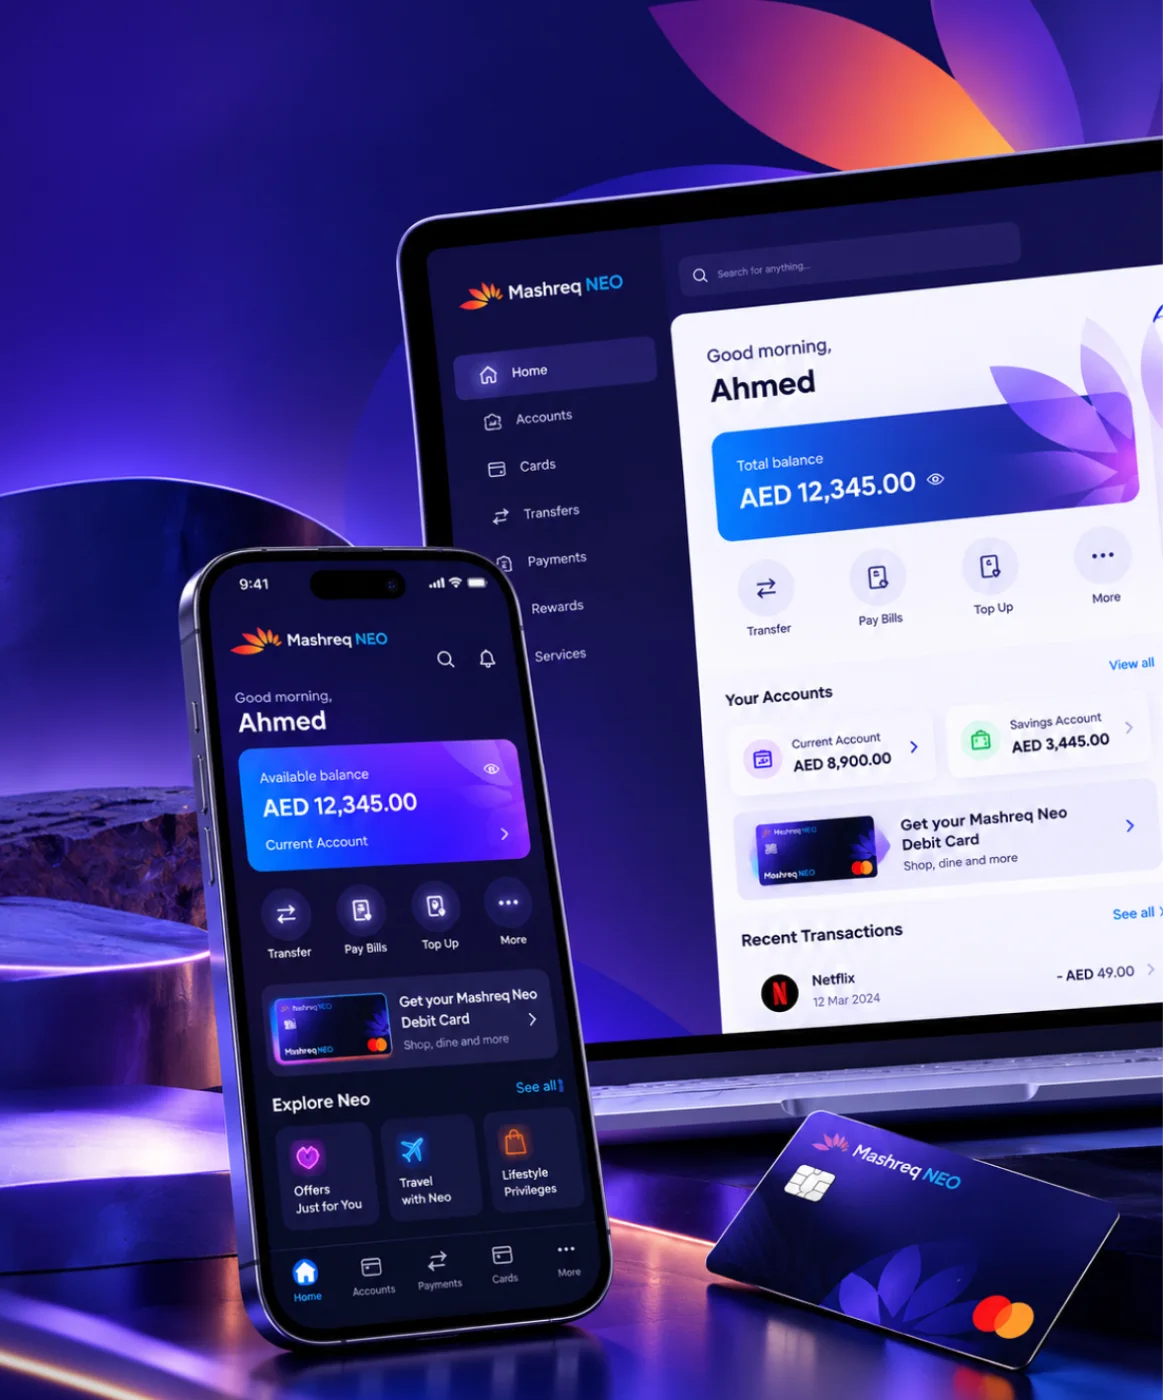
Six performance areas in one index for leadership, plus NEO GPT, a private assistant for bank documents.
Brands For Less
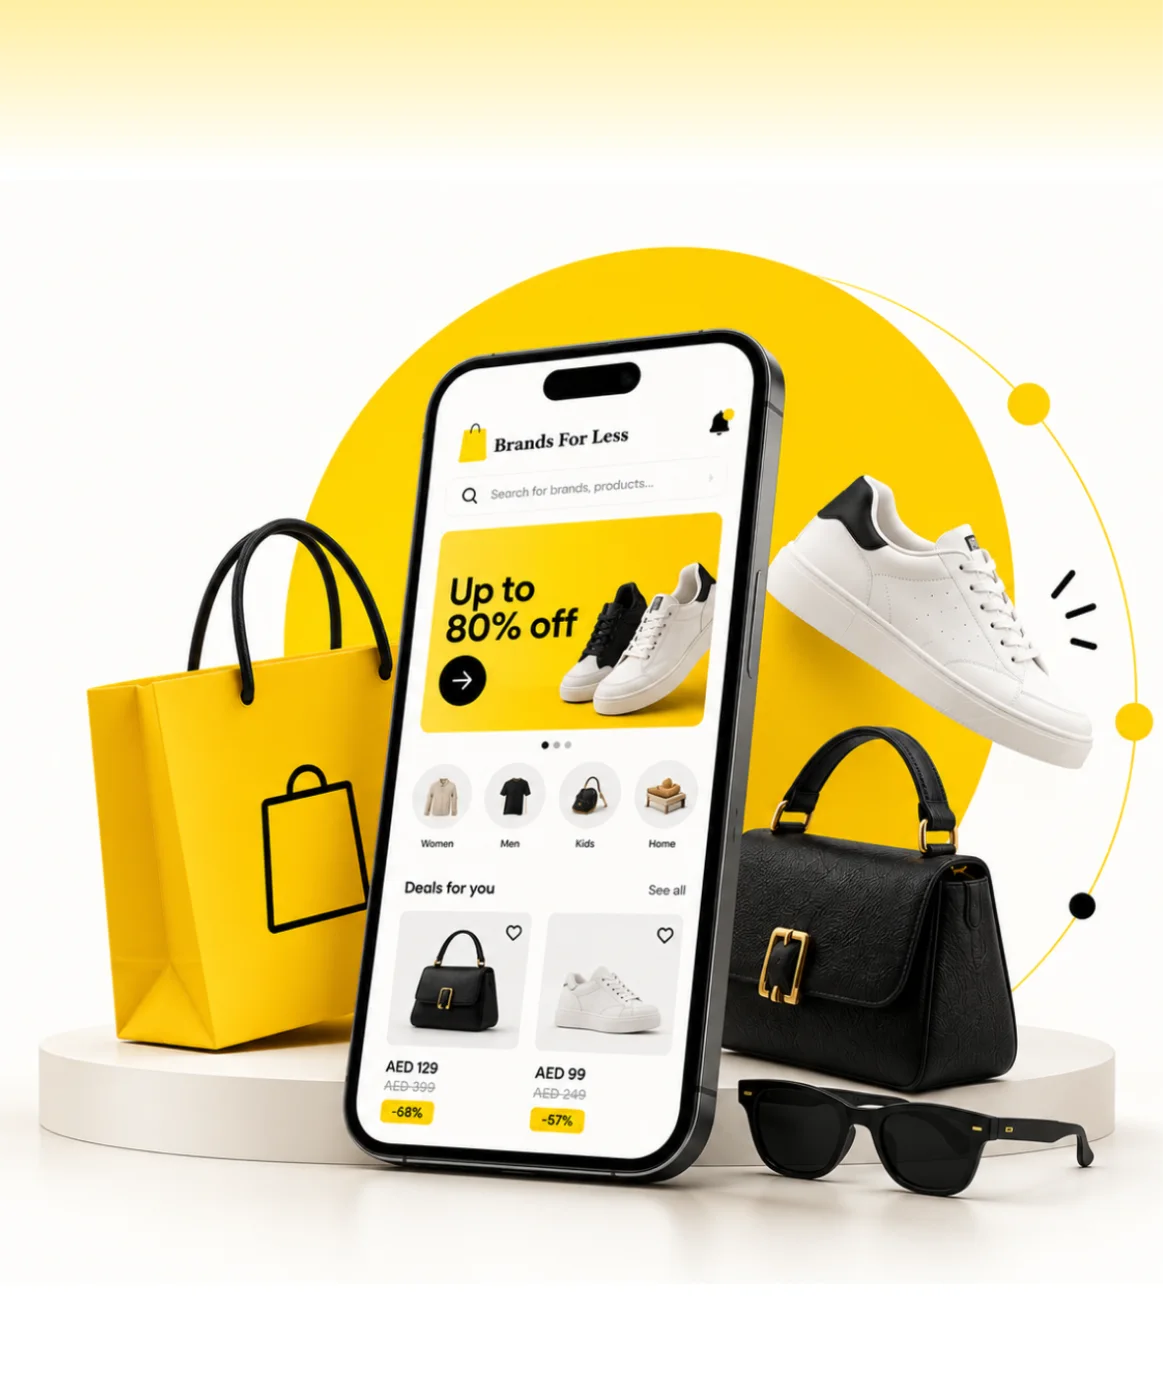
Found where shoppers dropped off, then redesigned sign-up, banners and cart for a retailer with 120+ stores.
Omantel
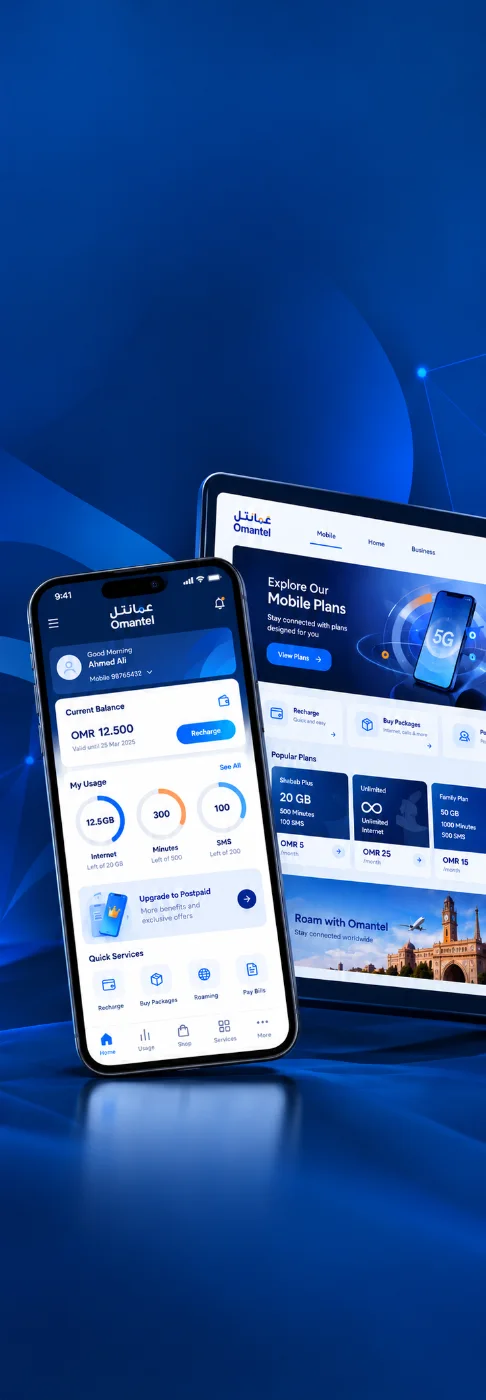
Incident, SLA and workload reporting in one Power BI suite for Oman’s first telecom operator.



Client Testimonials
Client Success: Panda
We reworked Panda's live app and website, from search to checkout, for shoppers across Saudi Arabia.
"Thanks to UIUX Studio’s work, the client successfully launched their websites. The team maintained a professional approach and scheduled frequent in-person meetings to provide suggestions for improving the project and ensuring its timely delivery."
 Shreya LadCEO, Nutroponics
"The team is well-versed in the UI/UX domain and has designed a fantastic journey to support the site’s growth projection. Communication, timeliness, and quality of work have been very professional."
 Mohammed AbdullahZeaara.com
"The Studio has been an absolute game changer for us. After working on a few independent projects, they are now also helping our marketing team, proving their value to our business and earning praise from executives."
 BrandonProject Manager
"The UIUX Studio team consistently delivers exceptional work with dedication. We’ve completed an amazing app design together, and I’m excited to collaborate with them again in the future."
 Hani Farajvancouverhousefinders.com
"We are really pleased with the work that UIUX Studio team has completed for us in designing a website for a new brand. They completed the designs quickly, took on board changes, and the finished product is very professional."
 AnayaHead of Marketing, Freshminds
"I’ve worked with UIUX Studio team on two projects. They capture the vision and run with it! They create exceptional design! Couldn’t be happier with the quality work and files for my developers."
 Brandon PugmirePresident, Imprint City
 Client Results
Reviewed on Upwork, Trustpilot, Clutch, G2 and GoodFirms


Work With Us
UIUX Studio offers flexible software development services with dedicated teams to meet your business needs. Whether you need an end-to-end build or specialised engineering expertise, our engagement models give you the support to launch and scale.
Access a dedicated team of engineers and QA, on-site or remote, focused on your product and your roadmap.
Get StartedGet clear, upfront pricing for a defined build, such as an MVP, an integration or a platform migration.
Get StartedGet expert engineers by the hour, perfect for code reviews, bug fixes, small features or architecture advice without a long-term commitment.
Get StartedTest count and coverage percentage are the two easiest numbers to game. None of these are.
Bugs reaching production that the suite should have caught. The number the whole engagement exists to reduce.
Share of runs failing for reasons unrelated to the change. Above a couple of per cent, people stop believing red.
How long feedback takes. A suite over ten minutes stops being run locally, which doubles the feedback loop.
How long a security or accessibility issue stays open. Findings that age were never really accepted.
Count and age, by severity. Trending rather than a snapshot, so drift is visible.
Deploys needing a fix or rollback. The clearest business-level signal that quality work is landing.
From retail apps and banking dashboards to a defence group rebrand, we bring proven domain knowledge to every product we design and build.
Talk to Our Team
Streaming, OTT & content platforms

Fan engagement & live data

EdTech & learning platforms

AdTech & campaign tooling

PropTech & marketplaces
Payments, banking & wealth

Digital health & patient apps
Retail & D2C platforms
Supply chain & fleet ops
B2B products & dashboards
Quality and security are cross-cutting, so this work is normally scoped alongside whatever is being built or run.
Applications built with tests and budgets enforced by the same gates from the first commit.
View service ↗The pipeline these gates live in, plus secrets management and infrastructure policy checks.
View service ↗Tenant isolation testing and the compliance evidence an enterprise buyer will demand.
View service ↗Contract testing, auth review and the adversarial testing a public API needs before launch.
View service ↗Forty-five minutes with a quality engineer. We will work out whether your suite is giving you a real signal, where your actual risk is uncovered, and what we would delete first. No deck, no audit fee.
Assess your test suiteBook a free consultation with our design, engineering and AI experts. Share your idea and we’ll come back within one business day with clear next steps.
Recognised By


Our Offices

UAE · Headquarters
Office OFF2-127, SMARK 2 Building, Plot No. 33-0, Ras Al Khor Industrial Second, Dubai, UAE

India
B-409, Bestech Business Tower, Sector 66, SAS Nagar, Punjab 160062

Australia
Tapleys Hill Road, Fulham Gardens, SA 5024