



Offshore / Onsite
Hire Dedicated Team
Access dedicated strategists and senior engineers, on-site or remote, who review your plans and stay on call while you decide.
Get StartedSecurity and compliance advisory: gap analysis against SOC 2, ISO 27001 or DORA, a threat model for the systems that matter, and remediation sequenced by real risk. Compliance and security overlap but are not the same thing, and confusing them is expensive in both directions.
Our Clients










Compliance certifies that controls exist and are followed. It does not certify that the controls address your actual threats. Four patterns produce a certificate and leave the risk in place.
A policy set that describes a company you are not, so staff work around it and the evidence becomes fiction at audit time.
Controls written for how your organisation actually operates, so following them is the path of least resistance rather than a compliance tax.
A fortnight of screenshots before each audit, every year, and no continuous assurance in between.
Evidence generated automatically from your systems, collected once and mapped to every framework that needs it.
Full attention on the framework checklist while the actual attack path — usually credentials or a third party — goes unexamined.
A threat model for your systems first, then framework mapping. The controls that matter get built rather than merely documented.
The simple findings closed, the structural ones deferred indefinitely, and the report reused in sales calls regardless.
Remediation sequenced by exploitability and impact, with effort costed so deferral is a decision rather than a drift.
One body of work that serves the auditor and the engineering team, because collecting evidence twice is how these programmes become resented.
The realistic attack paths against your systems and data, prioritised by likelihood and impact rather than by framework clause.
Current state against SOC 2, ISO 27001, DORA or your sector requirement, with each gap tied to a control and an owner.
Policies written for how you actually work, mapped across frameworks so one control satisfies several requirements.
What can be generated from your systems continuously rather than assembled by hand before each audit.
Sequenced by real risk with effort in engineering weeks, so the plan can enter a budget rather than a wish list.
The register, evidence map and narrative your assessor will ask for, prepared before the audit window opens.
Almost nobody commissions this work early. These are the events that make it unavoidable.
A prospect requires SOC 2 or ISO 27001 and the deal is waiting on it. The timeline is now commercial rather than technical.
A security review from a customer, and answering it honestly has surfaced gaps nobody had catalogued.
Financial services, health or critical infrastructure obligations that carry real consequences for non-compliance.
Something occurred, disclosure obligations were unclear, and the board wants an independent read on exposure.
Findings from an assessor, and a need to fix the structural ones rather than paper over them again.
Model use now requires classification, documentation and oversight that does not currently exist.
Compliance work is dominated by cross-referencing: hundreds of control requirements against your policies, configurations and existing evidence, then the same exercise again for the second framework. Doing that at volume rather than by sample is what turns a three-month readiness project into three or four weeks, and the saving lands in your fee rather than ours.
Requirements mapped across SOC 2, ISO 27001 and DORA simultaneously, so a single control satisfies several clauses and evidence is collected once.
IAM policies, security groups, encryption settings and logging configuration assessed across every account rather than spot-checked.
Policies drafted against your actual architecture and sector, then rewritten with your security lead. Template policies are why staff work around them.
What risk your organisation tolerates, and what a finding is genuinely worth fixing, are governance decisions with accountability attached. Penetration testing is manual, because the vulnerabilities that matter are chains no scanner reports.
See our AI practiceAutomated scanning is a floor. The findings that matter are multi-step authorisation and logic flaws, found by someone thinking adversarially.
Confirmed exploitable in your context first. Unverified findings destroy the credibility of the whole assessment.
A drafted policy is a starting point for a conversation with security, legal and the people who have to follow it.
Where you choose to accept a risk, that decision is recorded with a named owner and a review date rather than left implicit.
Starting with the checklist produces a certificate and leaves the risk. Starting with the threat model produces controls that matter and satisfies the framework as a consequence rather than as the goal.
What an attacker would actually go after, how, and what it would cost you. Credentials and third parties, not the exotic scenarios that make better slides.
IAM, network, encryption, logging, access reviews and change management across the whole estate, plus whatever policies already exist.
Gaps against every framework you need at once, so one control satisfies several requirements and evidence is not collected twice.
Policies drafted against how you actually operate, then worked through with security, legal and the teams affected. A policy nobody follows is a liability at audit.
Remediation ordered by exploitability and impact with effort in engineering weeks, plus the register and evidence map your assessor will ask for.
Read-only access under NDA, with the register, policies and evidence automation left running in your accounts.



Read-only access under NDA, with the register, policies and evidence automation left running in your accounts.



Read-only access under NDA, with the register, policies and evidence automation left running in your accounts.


Read-only access under NDA, with the register, policies and evidence automation left running in your accounts.


Read-only access under NDA, with the register, policies and evidence automation left running in your accounts.



Case Studies
Selected work for retail, banking, telecom and defence teams, from brand identity and mobile apps to data platforms and AI assistants.
Panda
Reworked search, categories and checkout in Panda’s live app and website, in Arabic and English.
EDGE Group
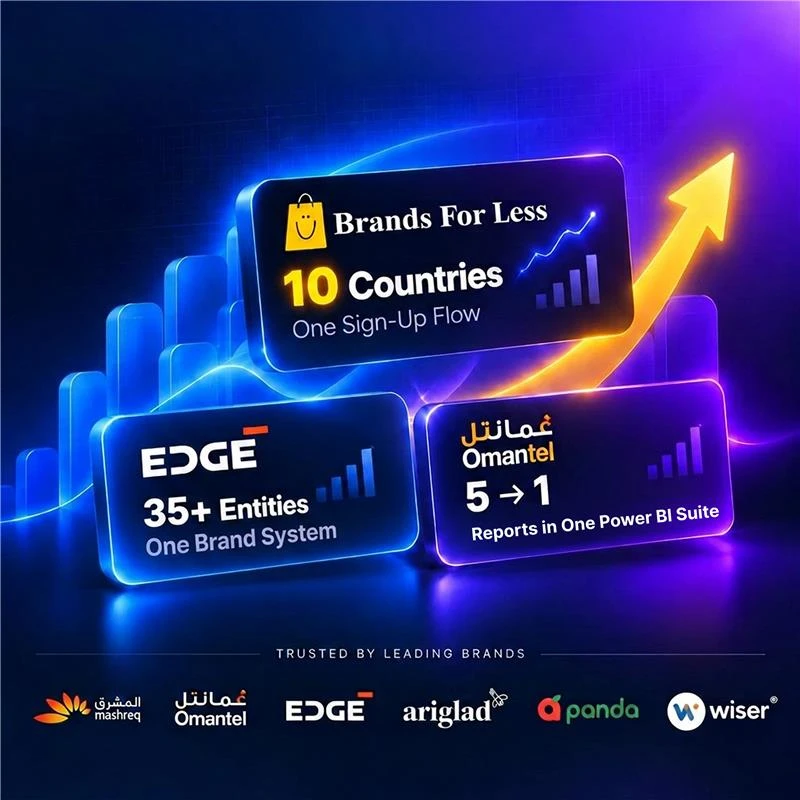
Brand identity, website and print for a group of 12,000 staff, carried onto the IDEX show floor.
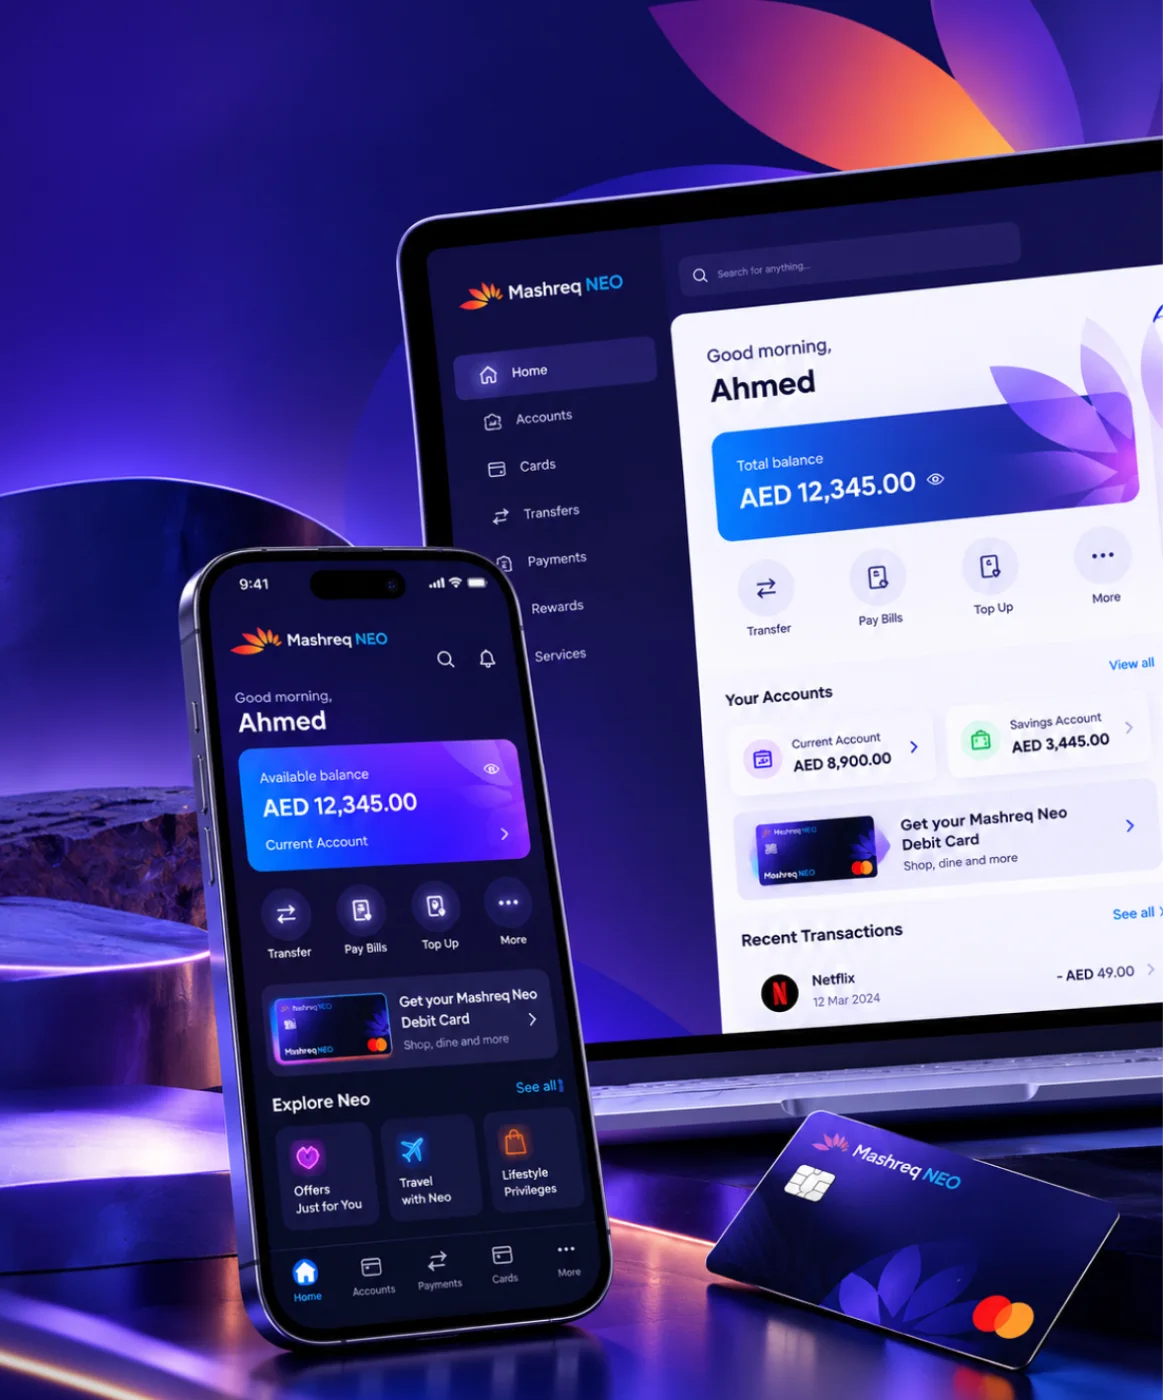
Mashreq NEO
Six performance areas in one index for leadership, plus NEO GPT, a private assistant for bank documents.
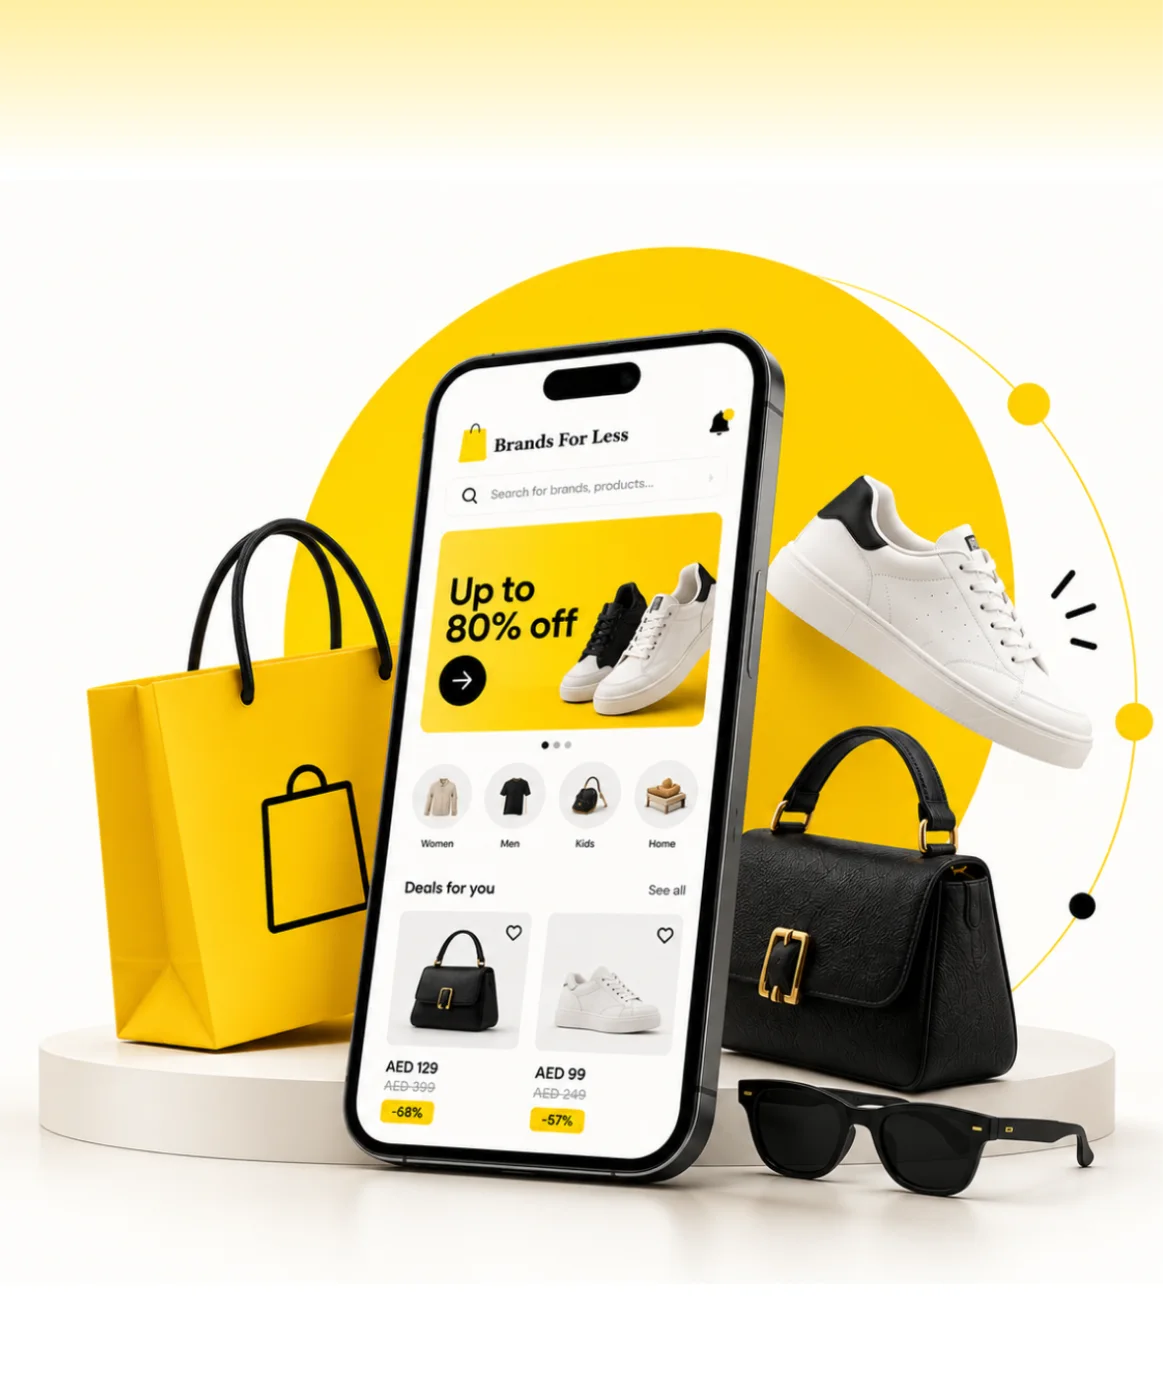
Brands For Less
Found where shoppers dropped off, then redesigned sign-up, banners and cart for a retailer with 120+ stores.
Omantel
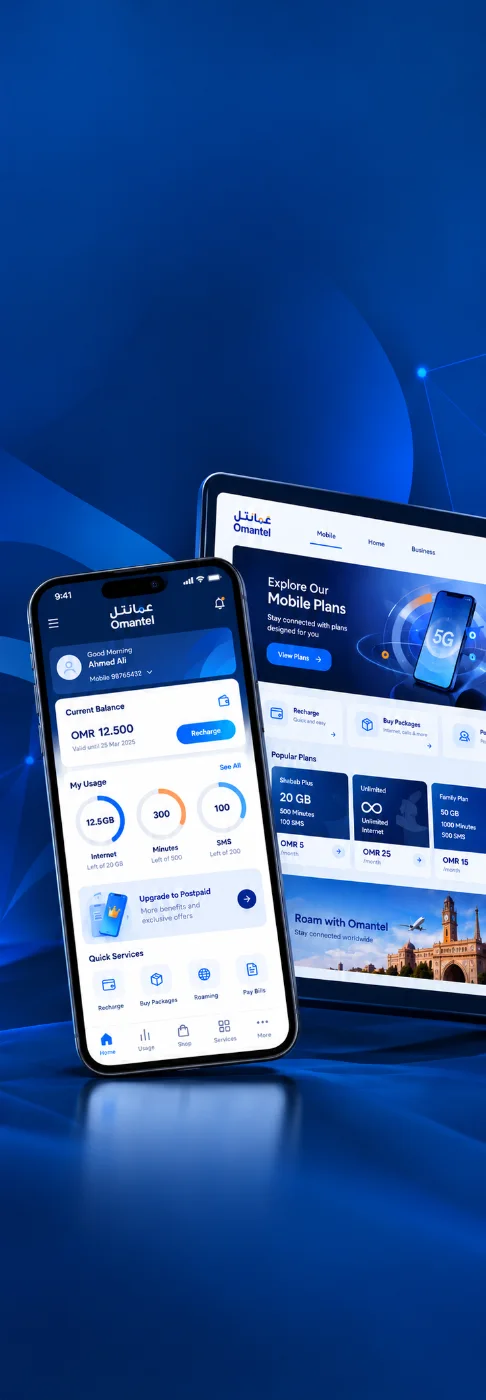
Incident, SLA and workload reporting in one Power BI suite for Oman’s first telecom operator.



Client Testimonials
Client Success: Panda
We reworked Panda's live app and website, from search to checkout, for shoppers across Saudi Arabia.
"Thanks to UIUX Studio’s work, the client successfully launched their websites. The team maintained a professional approach and scheduled frequent in-person meetings to provide suggestions for improving the project and ensuring its timely delivery."
 Shreya LadCEO, Nutroponics
"The team is well-versed in the UI/UX domain and has designed a fantastic journey to support the site’s growth projection. Communication, timeliness, and quality of work have been very professional."
 Mohammed AbdullahZeaara.com
"The Studio has been an absolute game changer for us. After working on a few independent projects, they are now also helping our marketing team, proving their value to our business and earning praise from executives."
 BrandonProject Manager
"The UIUX Studio team consistently delivers exceptional work with dedication. We’ve completed an amazing app design together, and I’m excited to collaborate with them again in the future."
 Hani Farajvancouverhousefinders.com
"We are really pleased with the work that UIUX Studio team has completed for us in designing a website for a new brand. They completed the designs quickly, took on board changes, and the finished product is very professional."
 AnayaHead of Marketing, Freshminds
"I’ve worked with UIUX Studio team on two projects. They capture the vision and run with it! They create exceptional design! Couldn’t be happier with the quality work and files for my developers."
 Brandon PugmirePresident, Imprint City
 Client Results
Reviewed on Upwork, Trustpilot, Clutch, G2 and GoodFirms


WORK WITH US
UIUX Studio offers flexible technology advisory with a dedicated team of strategists and senior engineers. Whether you need a full technology roadmap or a second opinion on one decision, our engagement models give you independent advice when you need it.
Access dedicated strategists and senior engineers, on-site or remote, who review your plans and stay on call while you decide.
Get StartedGet clear, upfront pricing for work such as an AI readiness review, product discovery or a vendor selection, with set deliverables.
Get StartedGet a strategist or senior engineer by the hour to review an architecture, a vendor or a project plan.
Get StartedA certificate is a lagging indicator. These tell you whether the controls are really operating.
Share of prioritised attack paths with an operating control. This matters more than framework percentage.
Findings raised by your assessor, and how many were structural rather than documentary.
Proportion of evidence generated continuously rather than assembled by hand. Manual evidence is where audits get stressful.
How long a security finding stays open by severity. Findings that age were never really accepted.
How long a customer security review takes to answer. A good register turns weeks into a day.
Whether accepted risks are revisited on schedule, or quietly became permanent without anyone deciding.
From retail apps and banking dashboards to a defence group rebrand, we bring proven domain knowledge to every product we design and build.
Talk to Our Team
Streaming, OTT & content platforms

Fan engagement & live data

EdTech & learning platforms

AdTech & campaign tooling

PropTech & marketplaces
Payments, banking & wealth

Digital health & patient apps
Retail & D2C platforms
Supply chain & fleet ops
B2B products & dashboards
Most compliance gaps are closed by engineering work, so this engagement hands over rather than standing alone.
Penetration testing, scanning in the pipeline and the remediation delivered and retested.
View service ↗Access control, secrets management, logging and the infrastructure policy checks an audit requires.
View service ↗Tenant isolation, audit trails and the enterprise controls a large customer will demand.
View service ↗Governance and classification for AI systems, where regulation is arriving faster than practice.
View service ↗Forty-five minutes with a security engineer. We will tell you which answers reveal a real gap, which are documentation, and how far you actually are from certification. No deck, no assessment fee.
Assess our readinessBook a free consultation with our design, engineering and AI experts. Share your idea and we’ll come back within one business day with clear next steps.
Recognised By


Our Offices

UAE · Headquarters
Office OFF2-127, SMARK 2 Building, Plot No. 33-0, Ras Al Khor Industrial Second, Dubai, UAE

India
B-409, Bestech Business Tower, Sector 66, SAS Nagar, Punjab 160062

Australia
Tapleys Hill Road, Fulham Gardens, SA 5024